

Cycode: rebuilding AppSec [OTS teams]
Meet the Cycode team in Warsaw. Learn how we build security tools and what kind of engineers vibe with us.

Software development is done by AI agents now.
At least, that’s how it feels when agents can build features autonomously and even help secure them by catching vulnerable dependencies, misconfigurations, and hardcoded secrets.
But it’s still up to human engineers to control what those agents can access, which tools they connect to, and whether sensitive data can leave the development environment in a prompt.
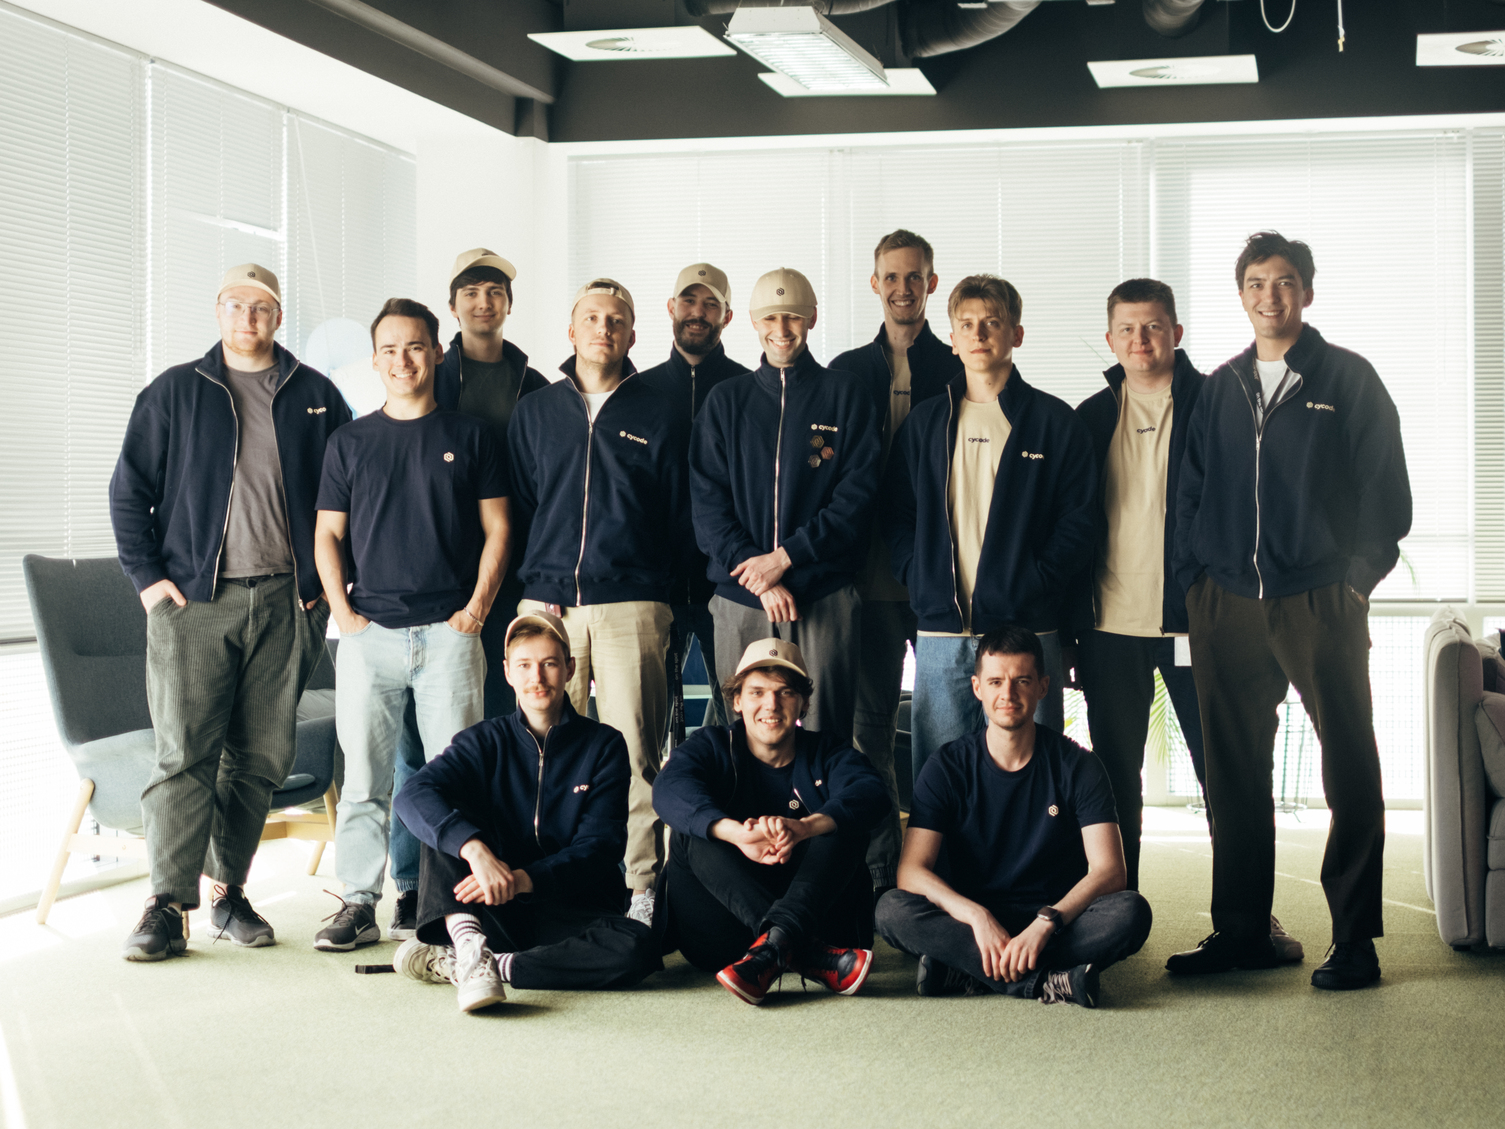
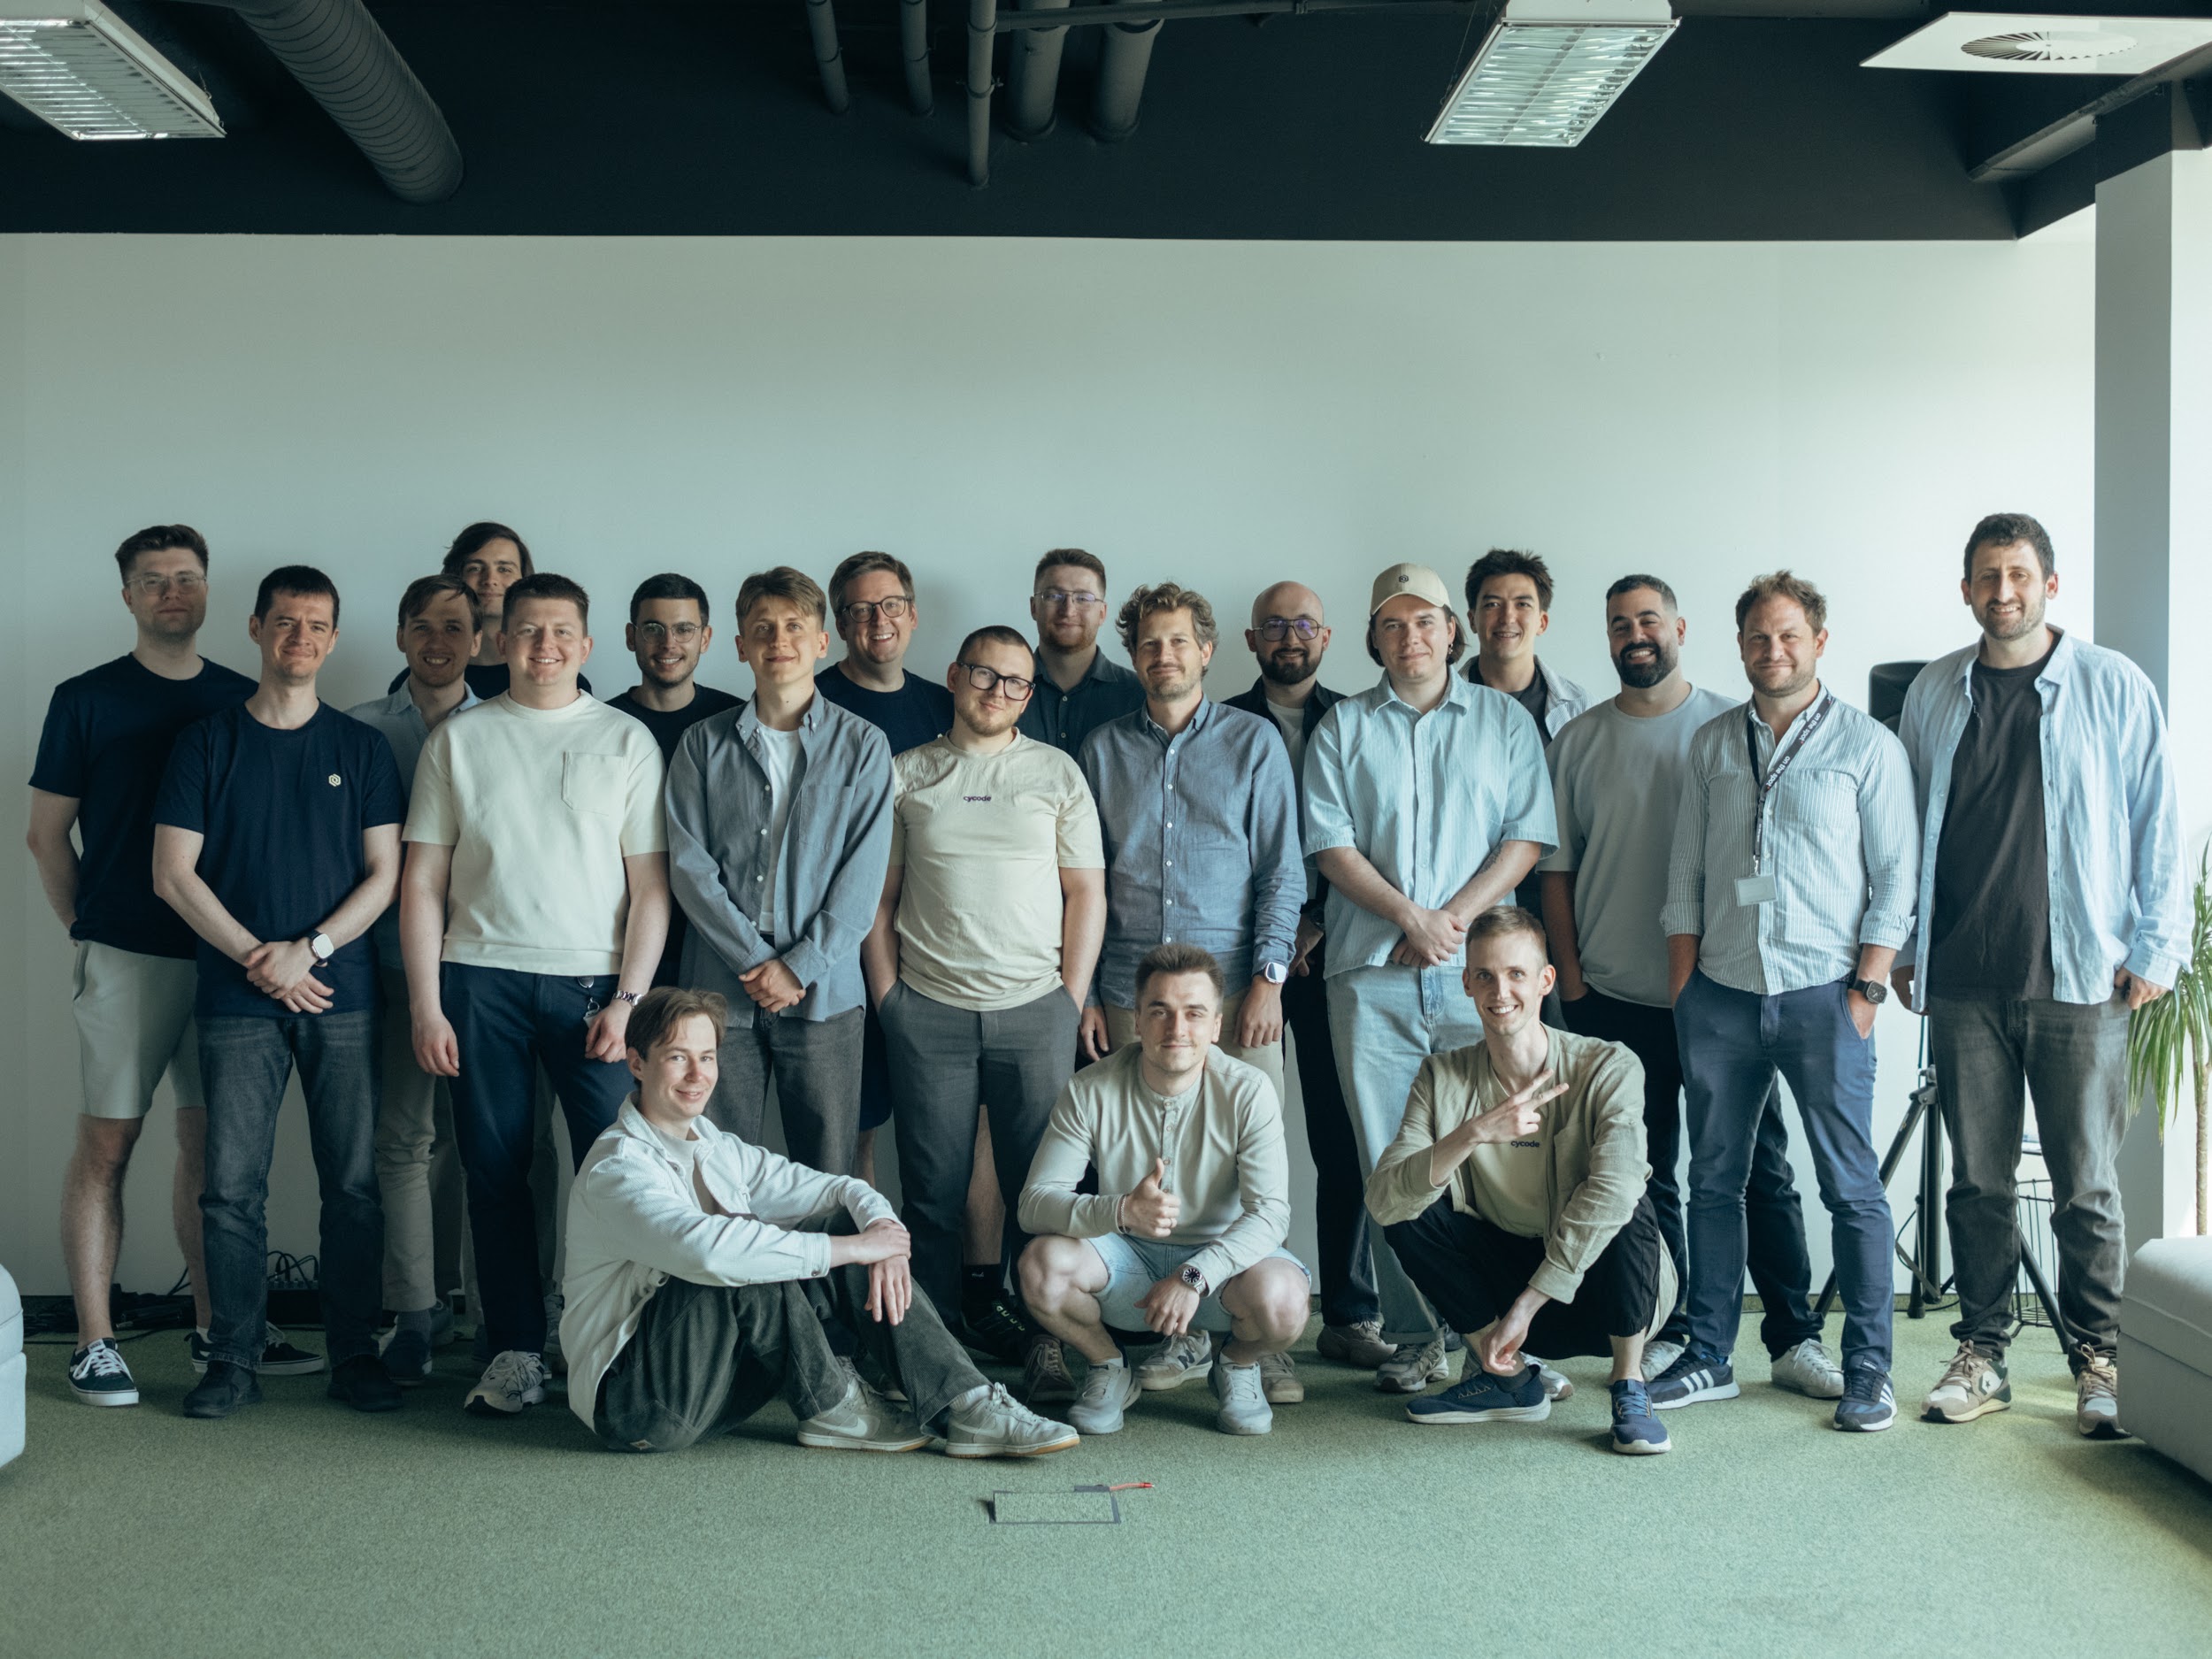
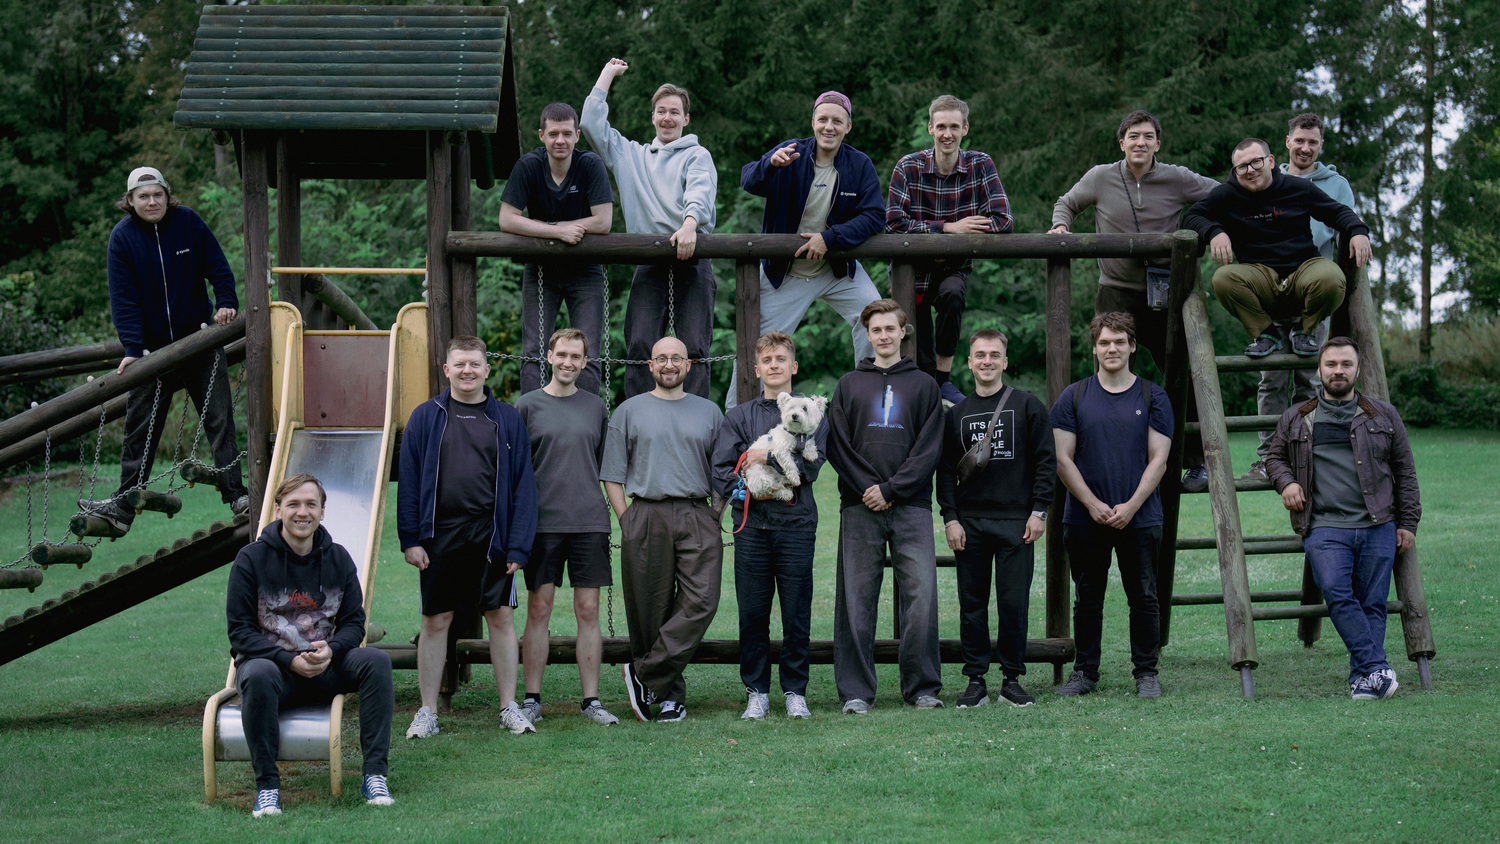
This is our Cycode team 👇
We sit in Warsaw and build a product that secures development from prompt to cloud — and makes life easier for our fellow engineers and ourselves.

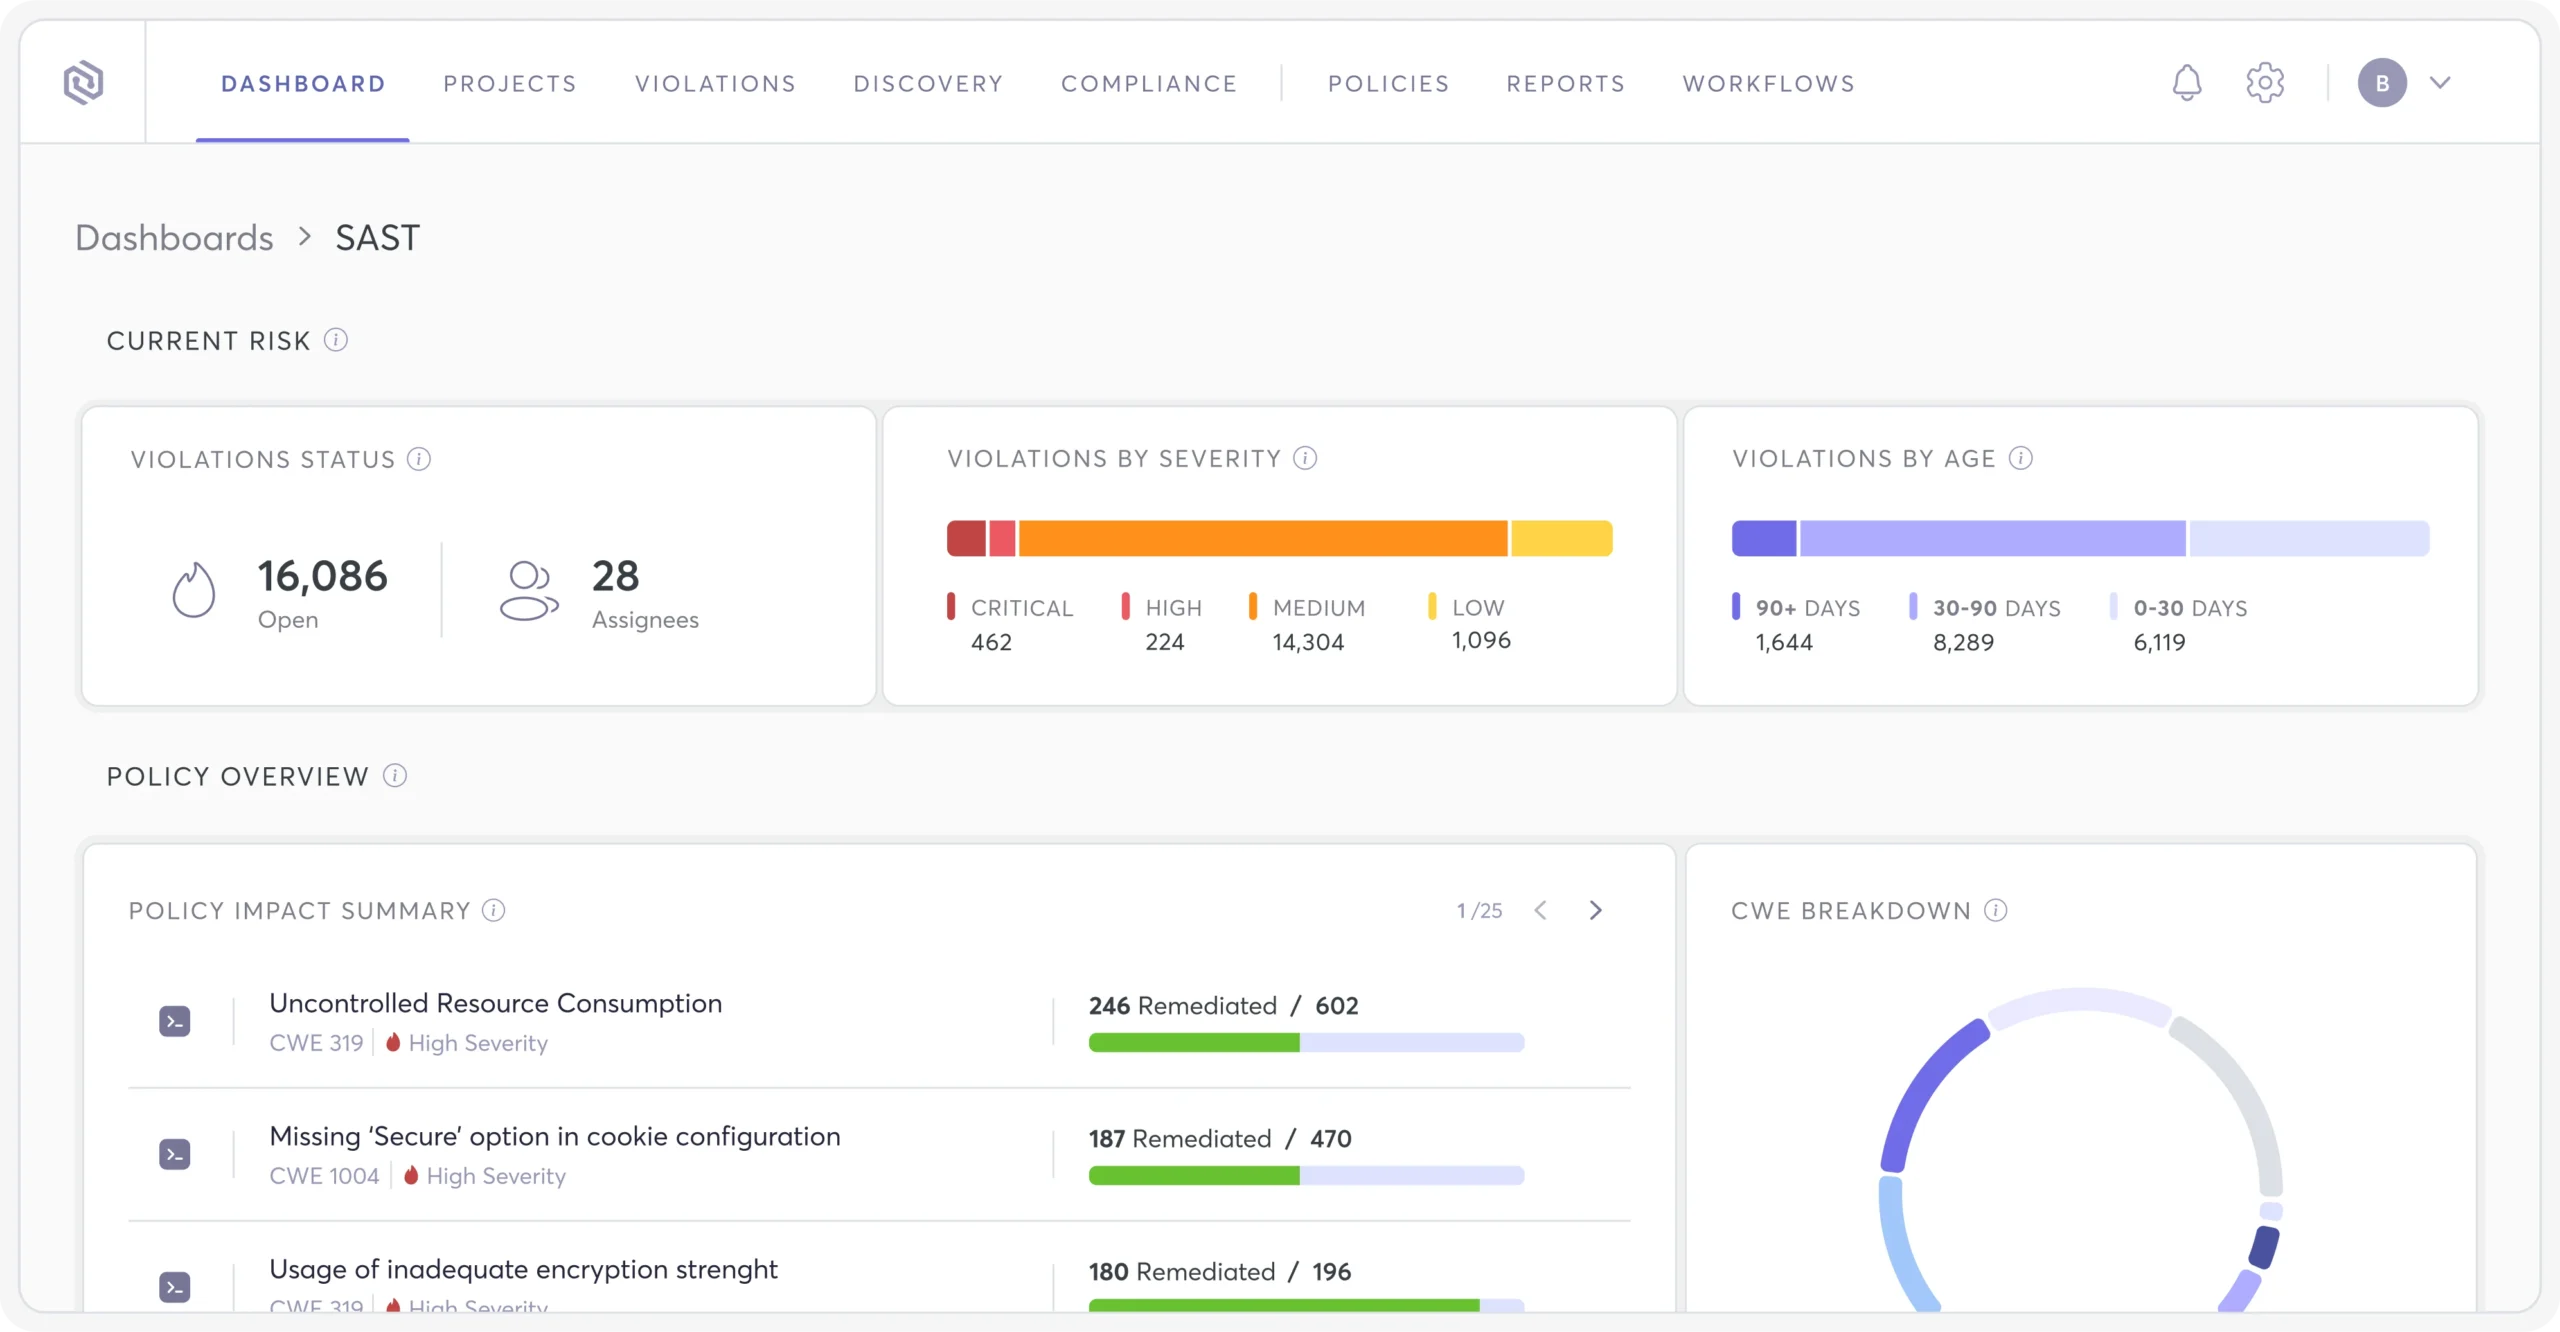
Our product: Agentic Development Security Platform
Cycode’s platform is designed to secure the entire software development lifecycle. It helps teams see which AI tools and agents are being used, define what they are allowed to do, detect AI-specific risks, and apply guardrails before risky actions cause security incidents.
Understanding Cycode’s anatomy
Two foundations are especially important:
1. Purpose-built native scanners
Cycode’s scanners are designed around the realities of modern development: monorepos, ephemeral environments, GitOps workflows, containerized applications, and AI-generated code.
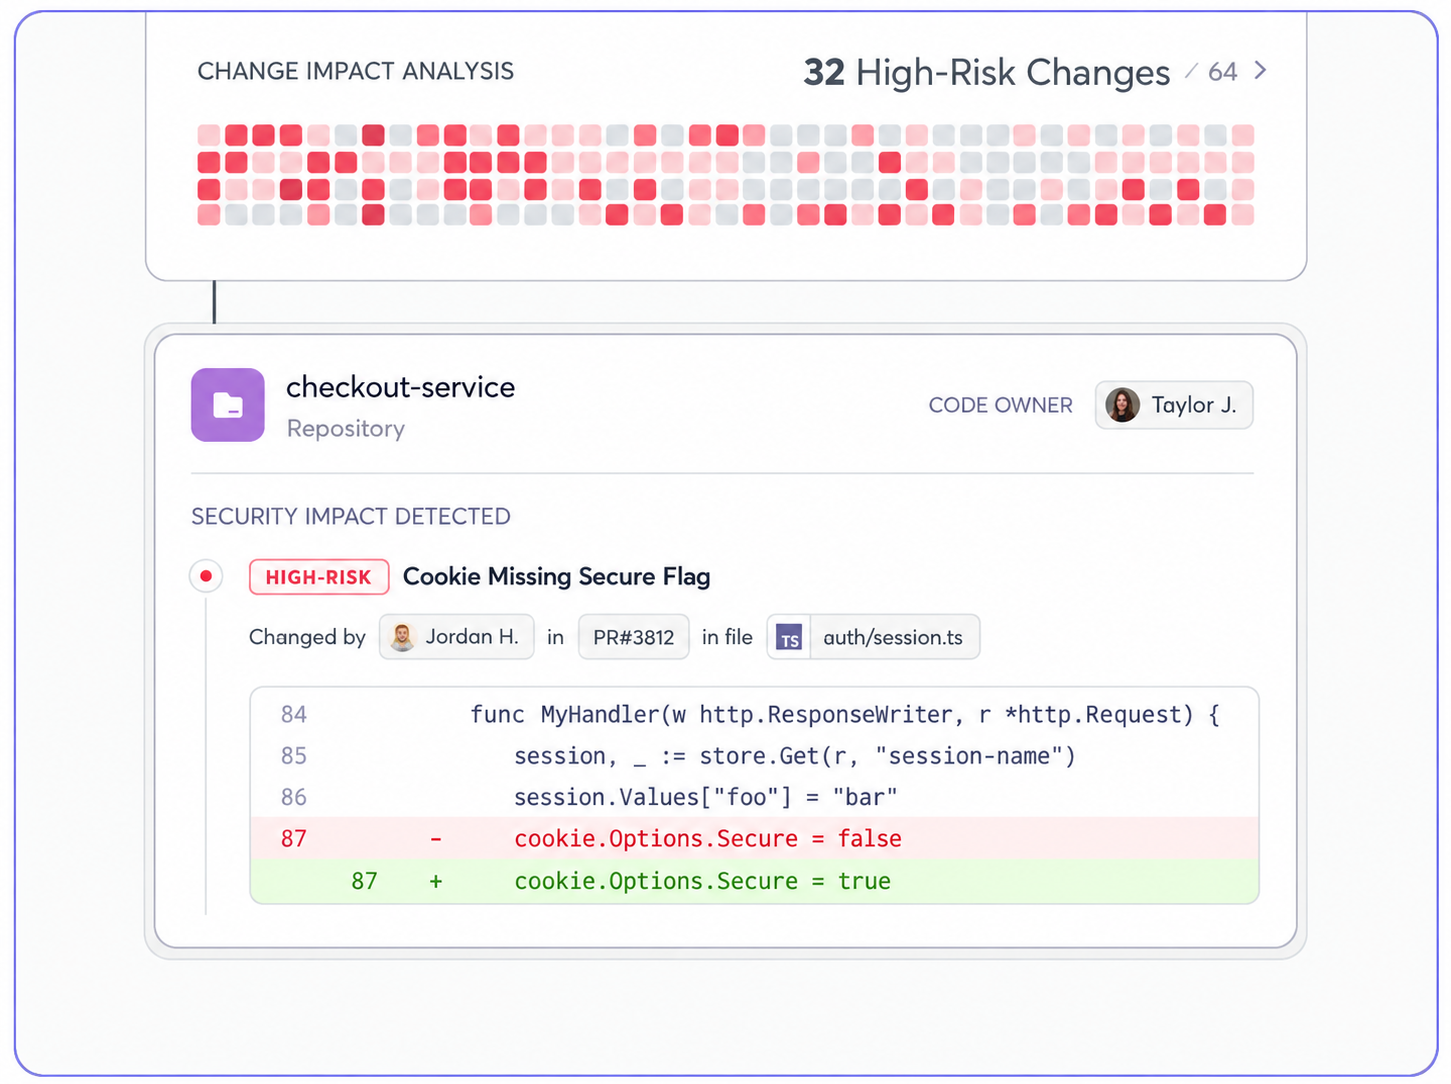
Take Static Application Security Testing (SAST). Instead of pointing to a suspicious line and leaving the developer to investigate, Cycode follows potentially unsafe data through the application, from where it enters to where it could reach a sensitive operation.
The engine does this without running the program. It creates a simplified map of the code and checks the possible routes through it.
[callout]
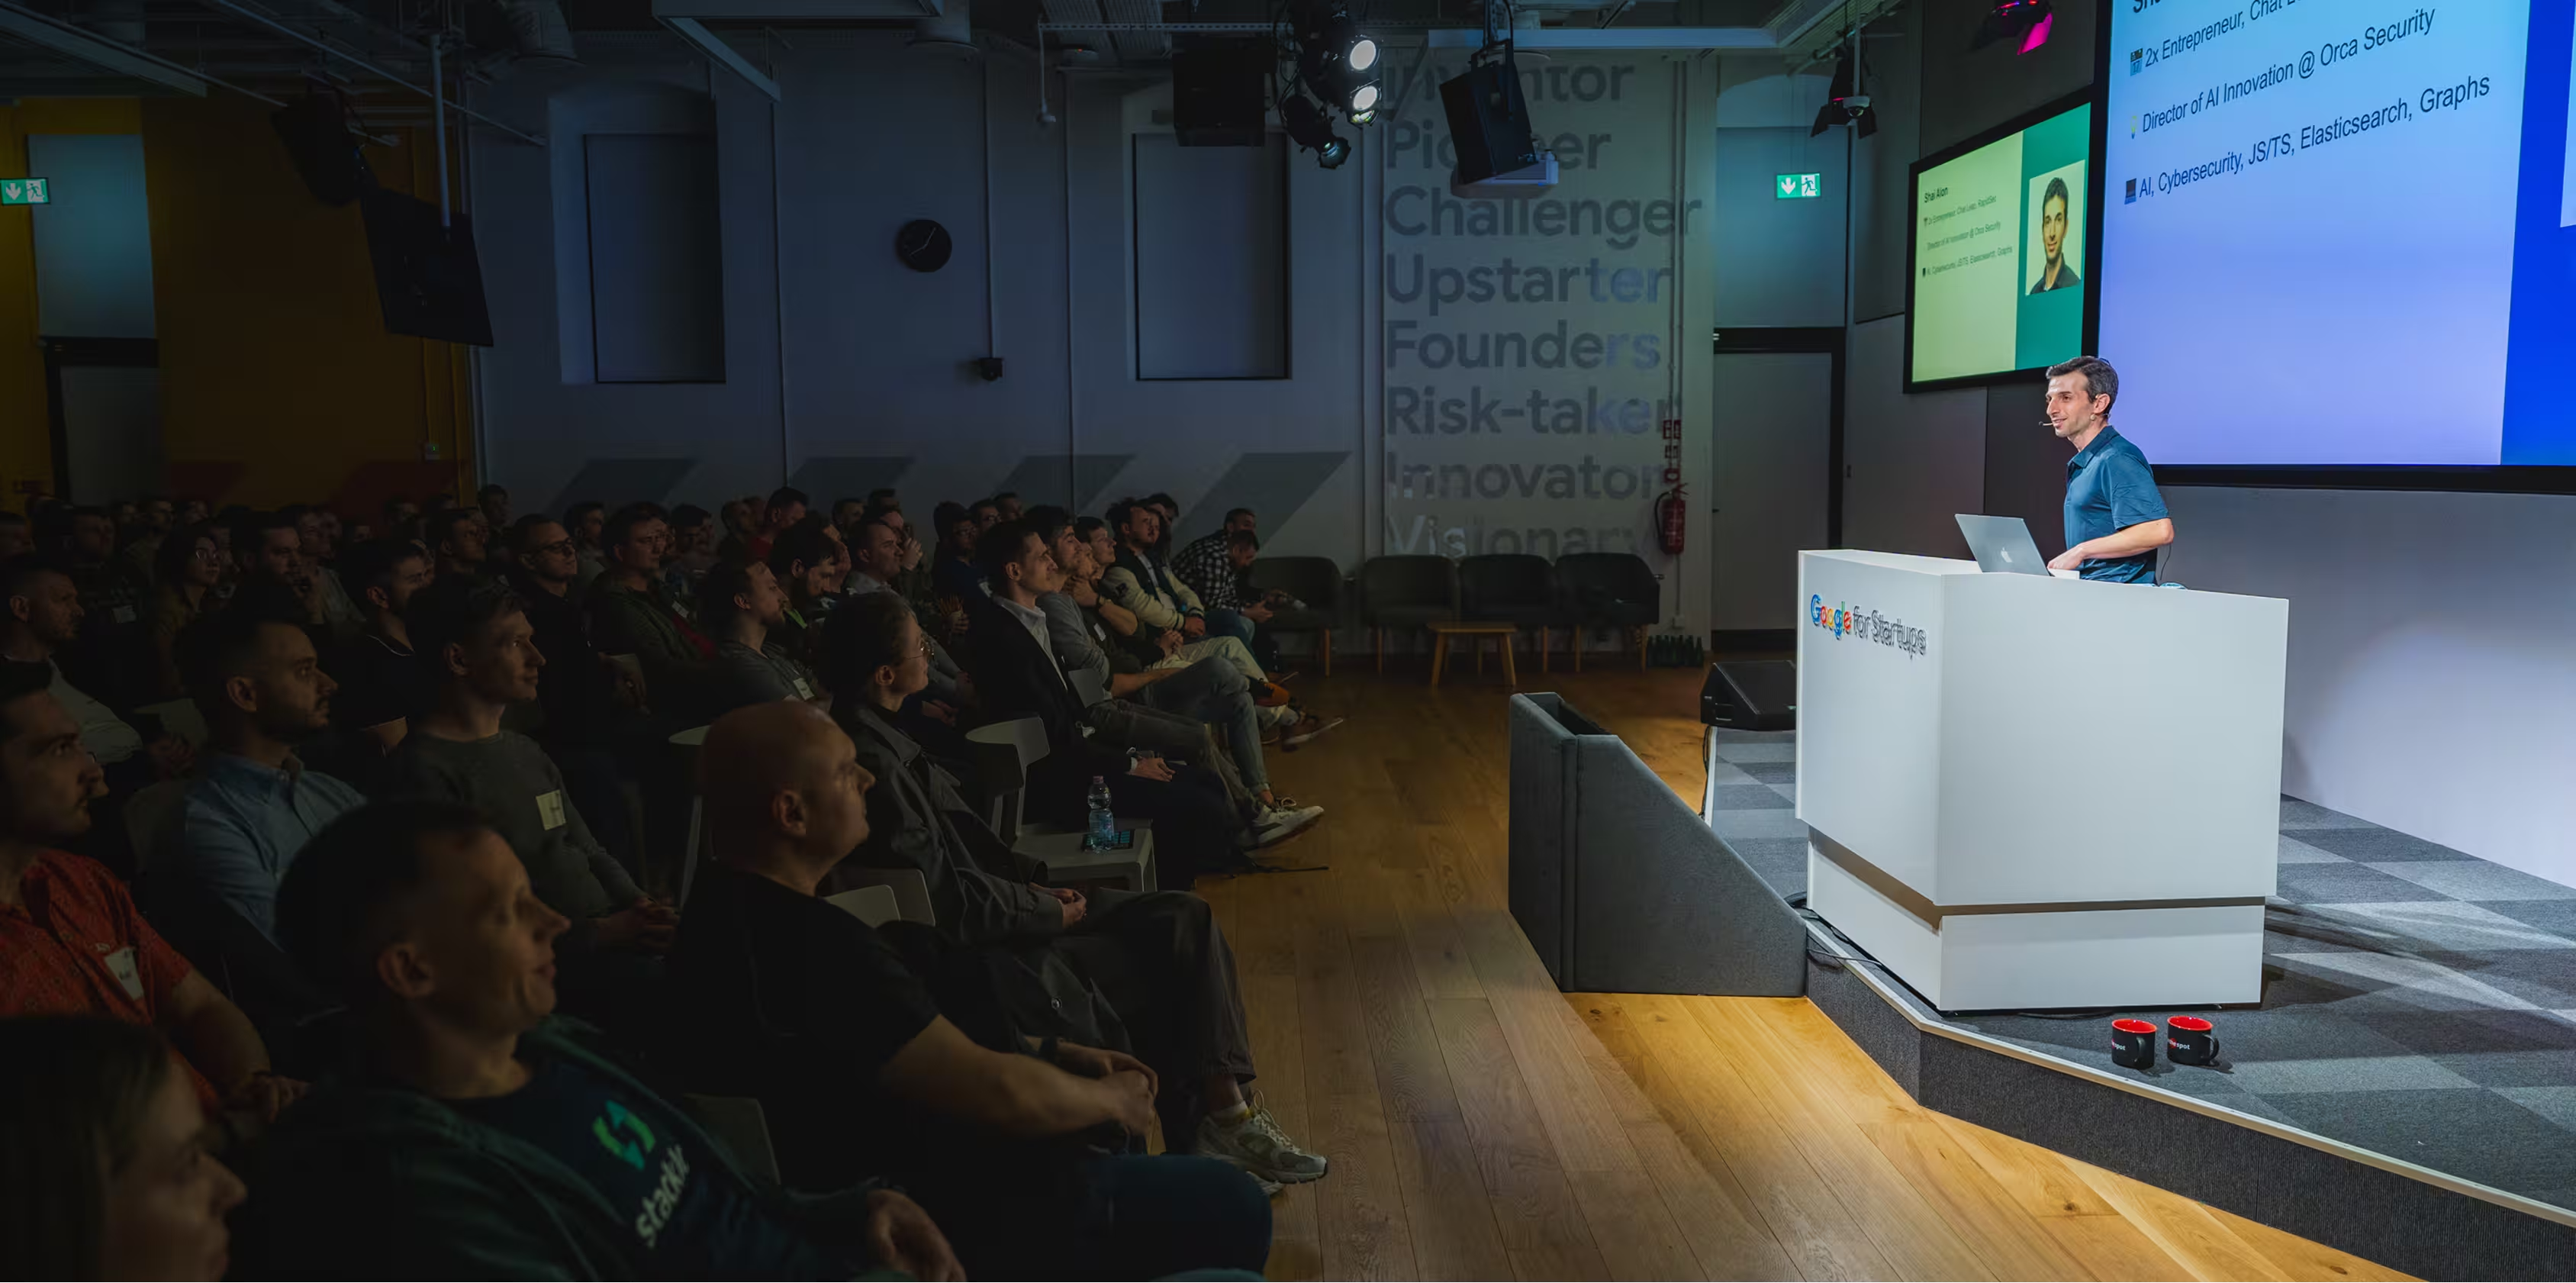
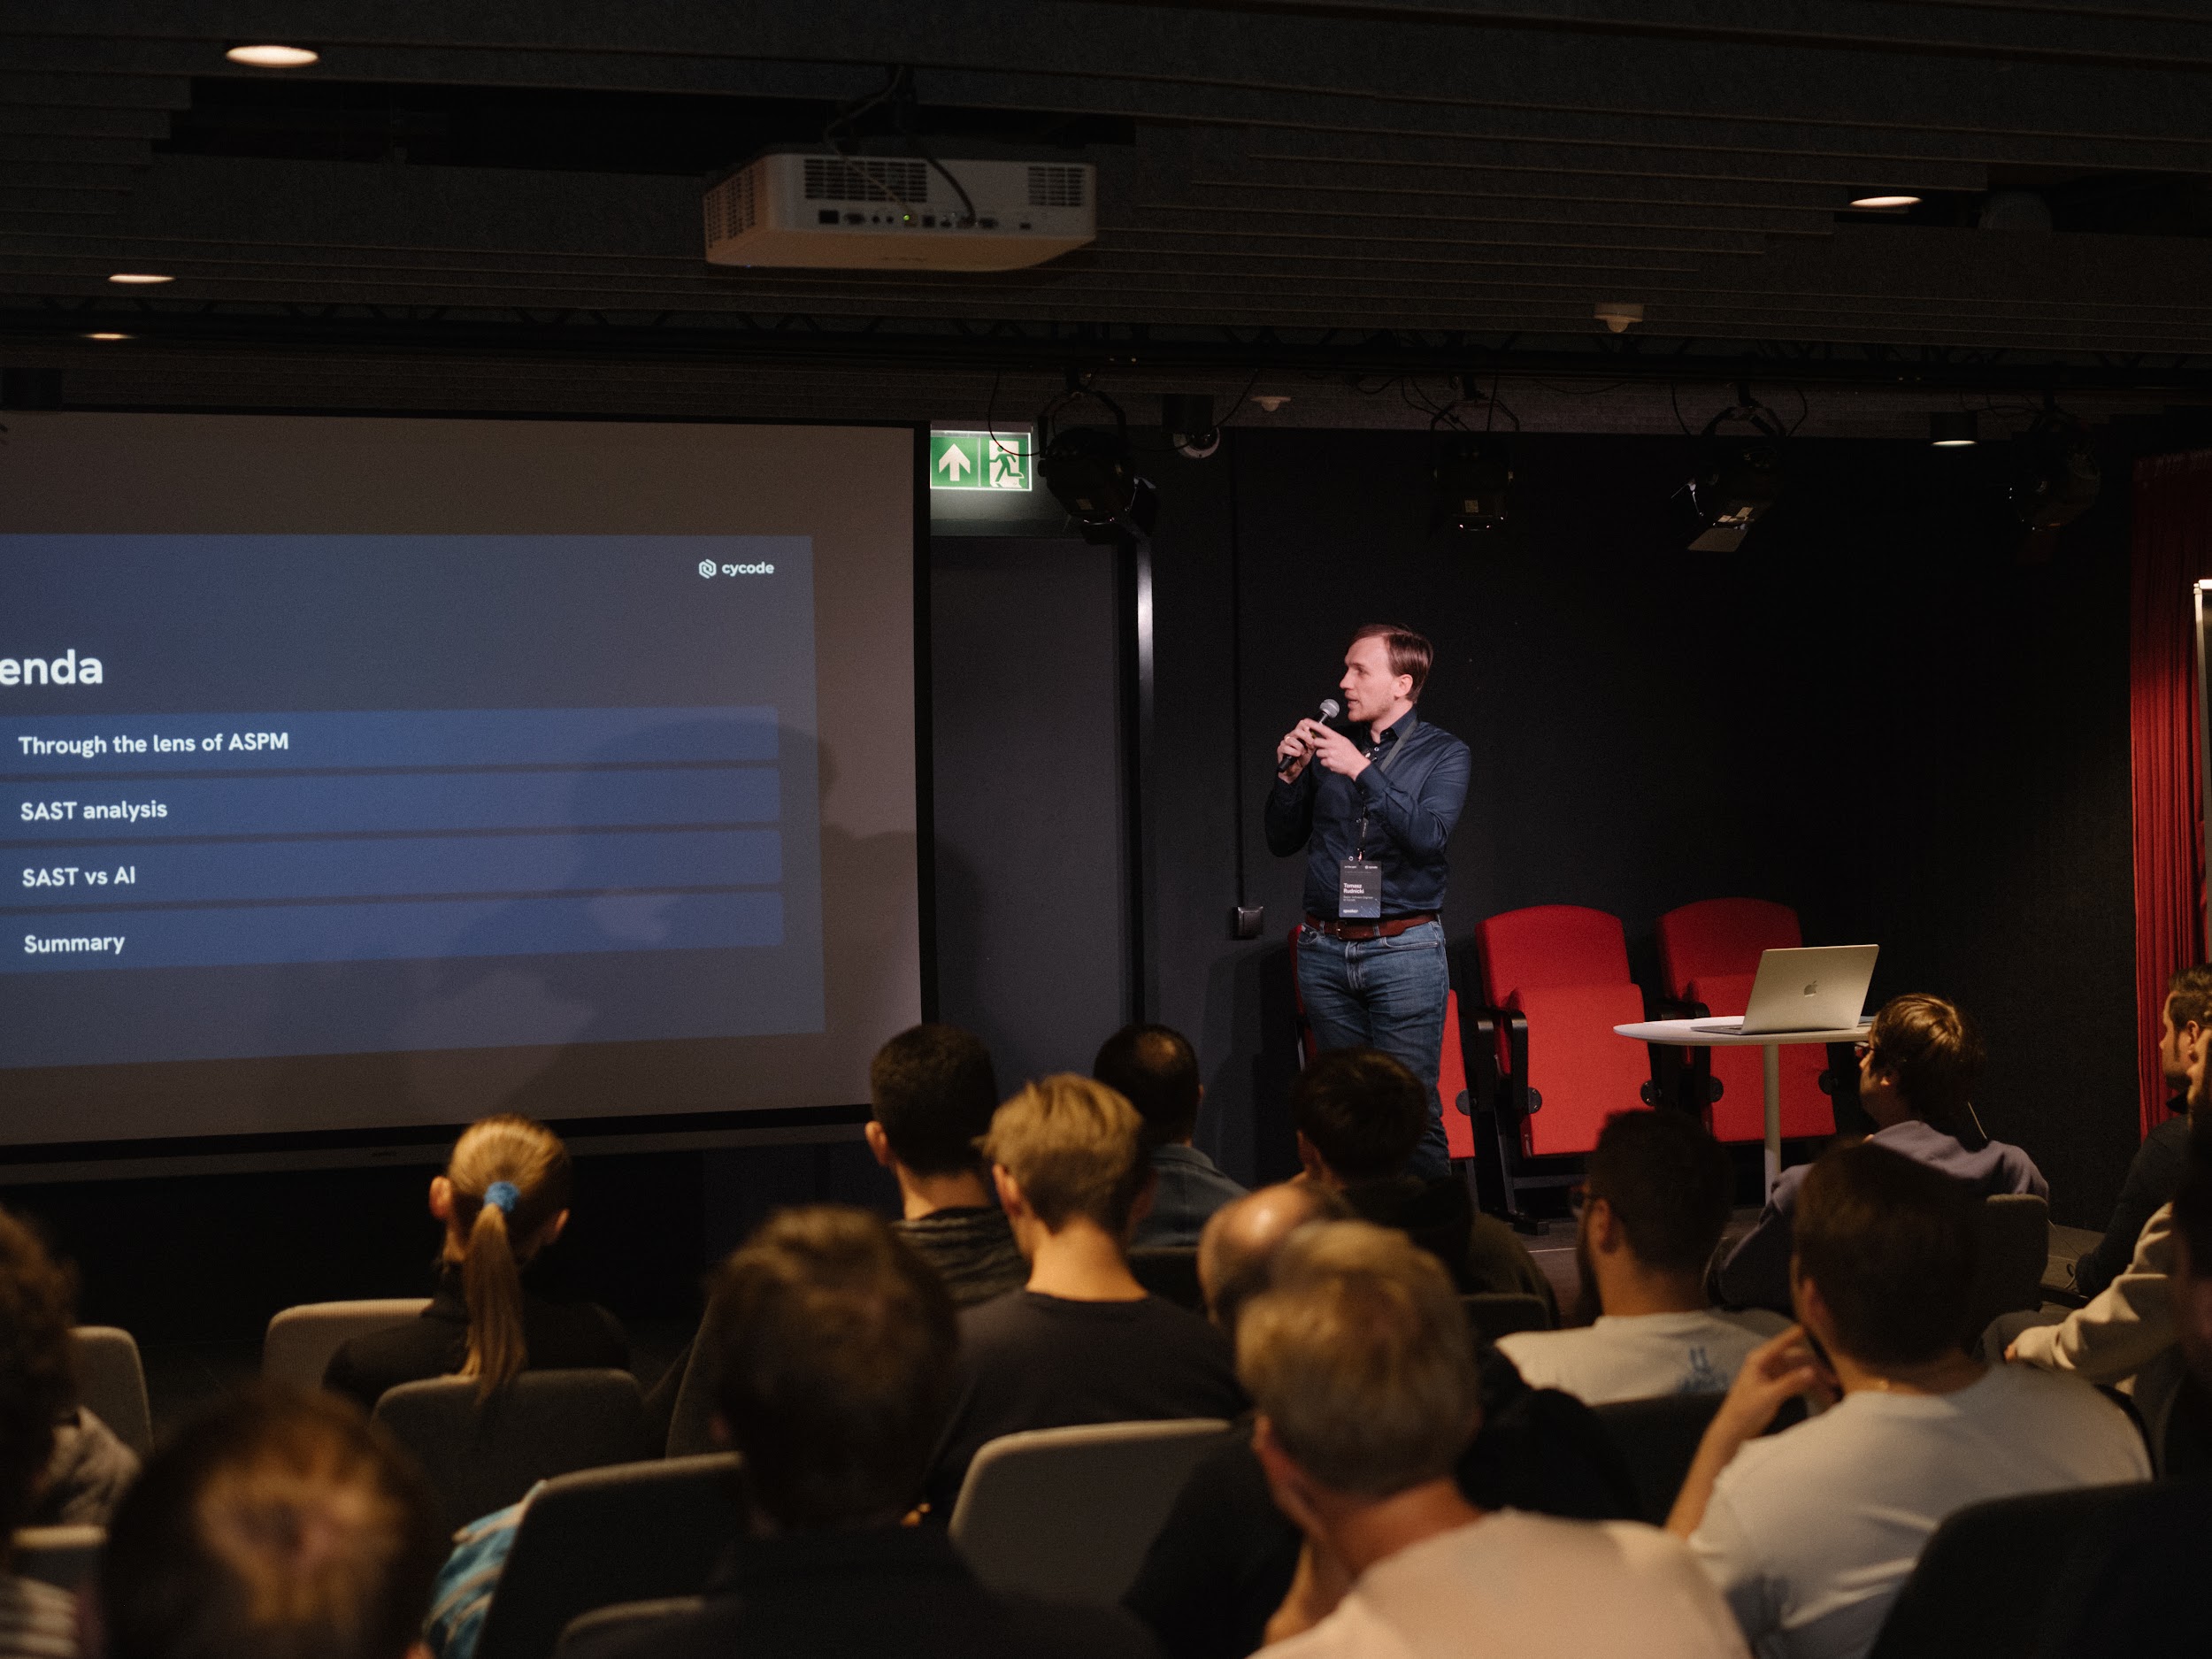
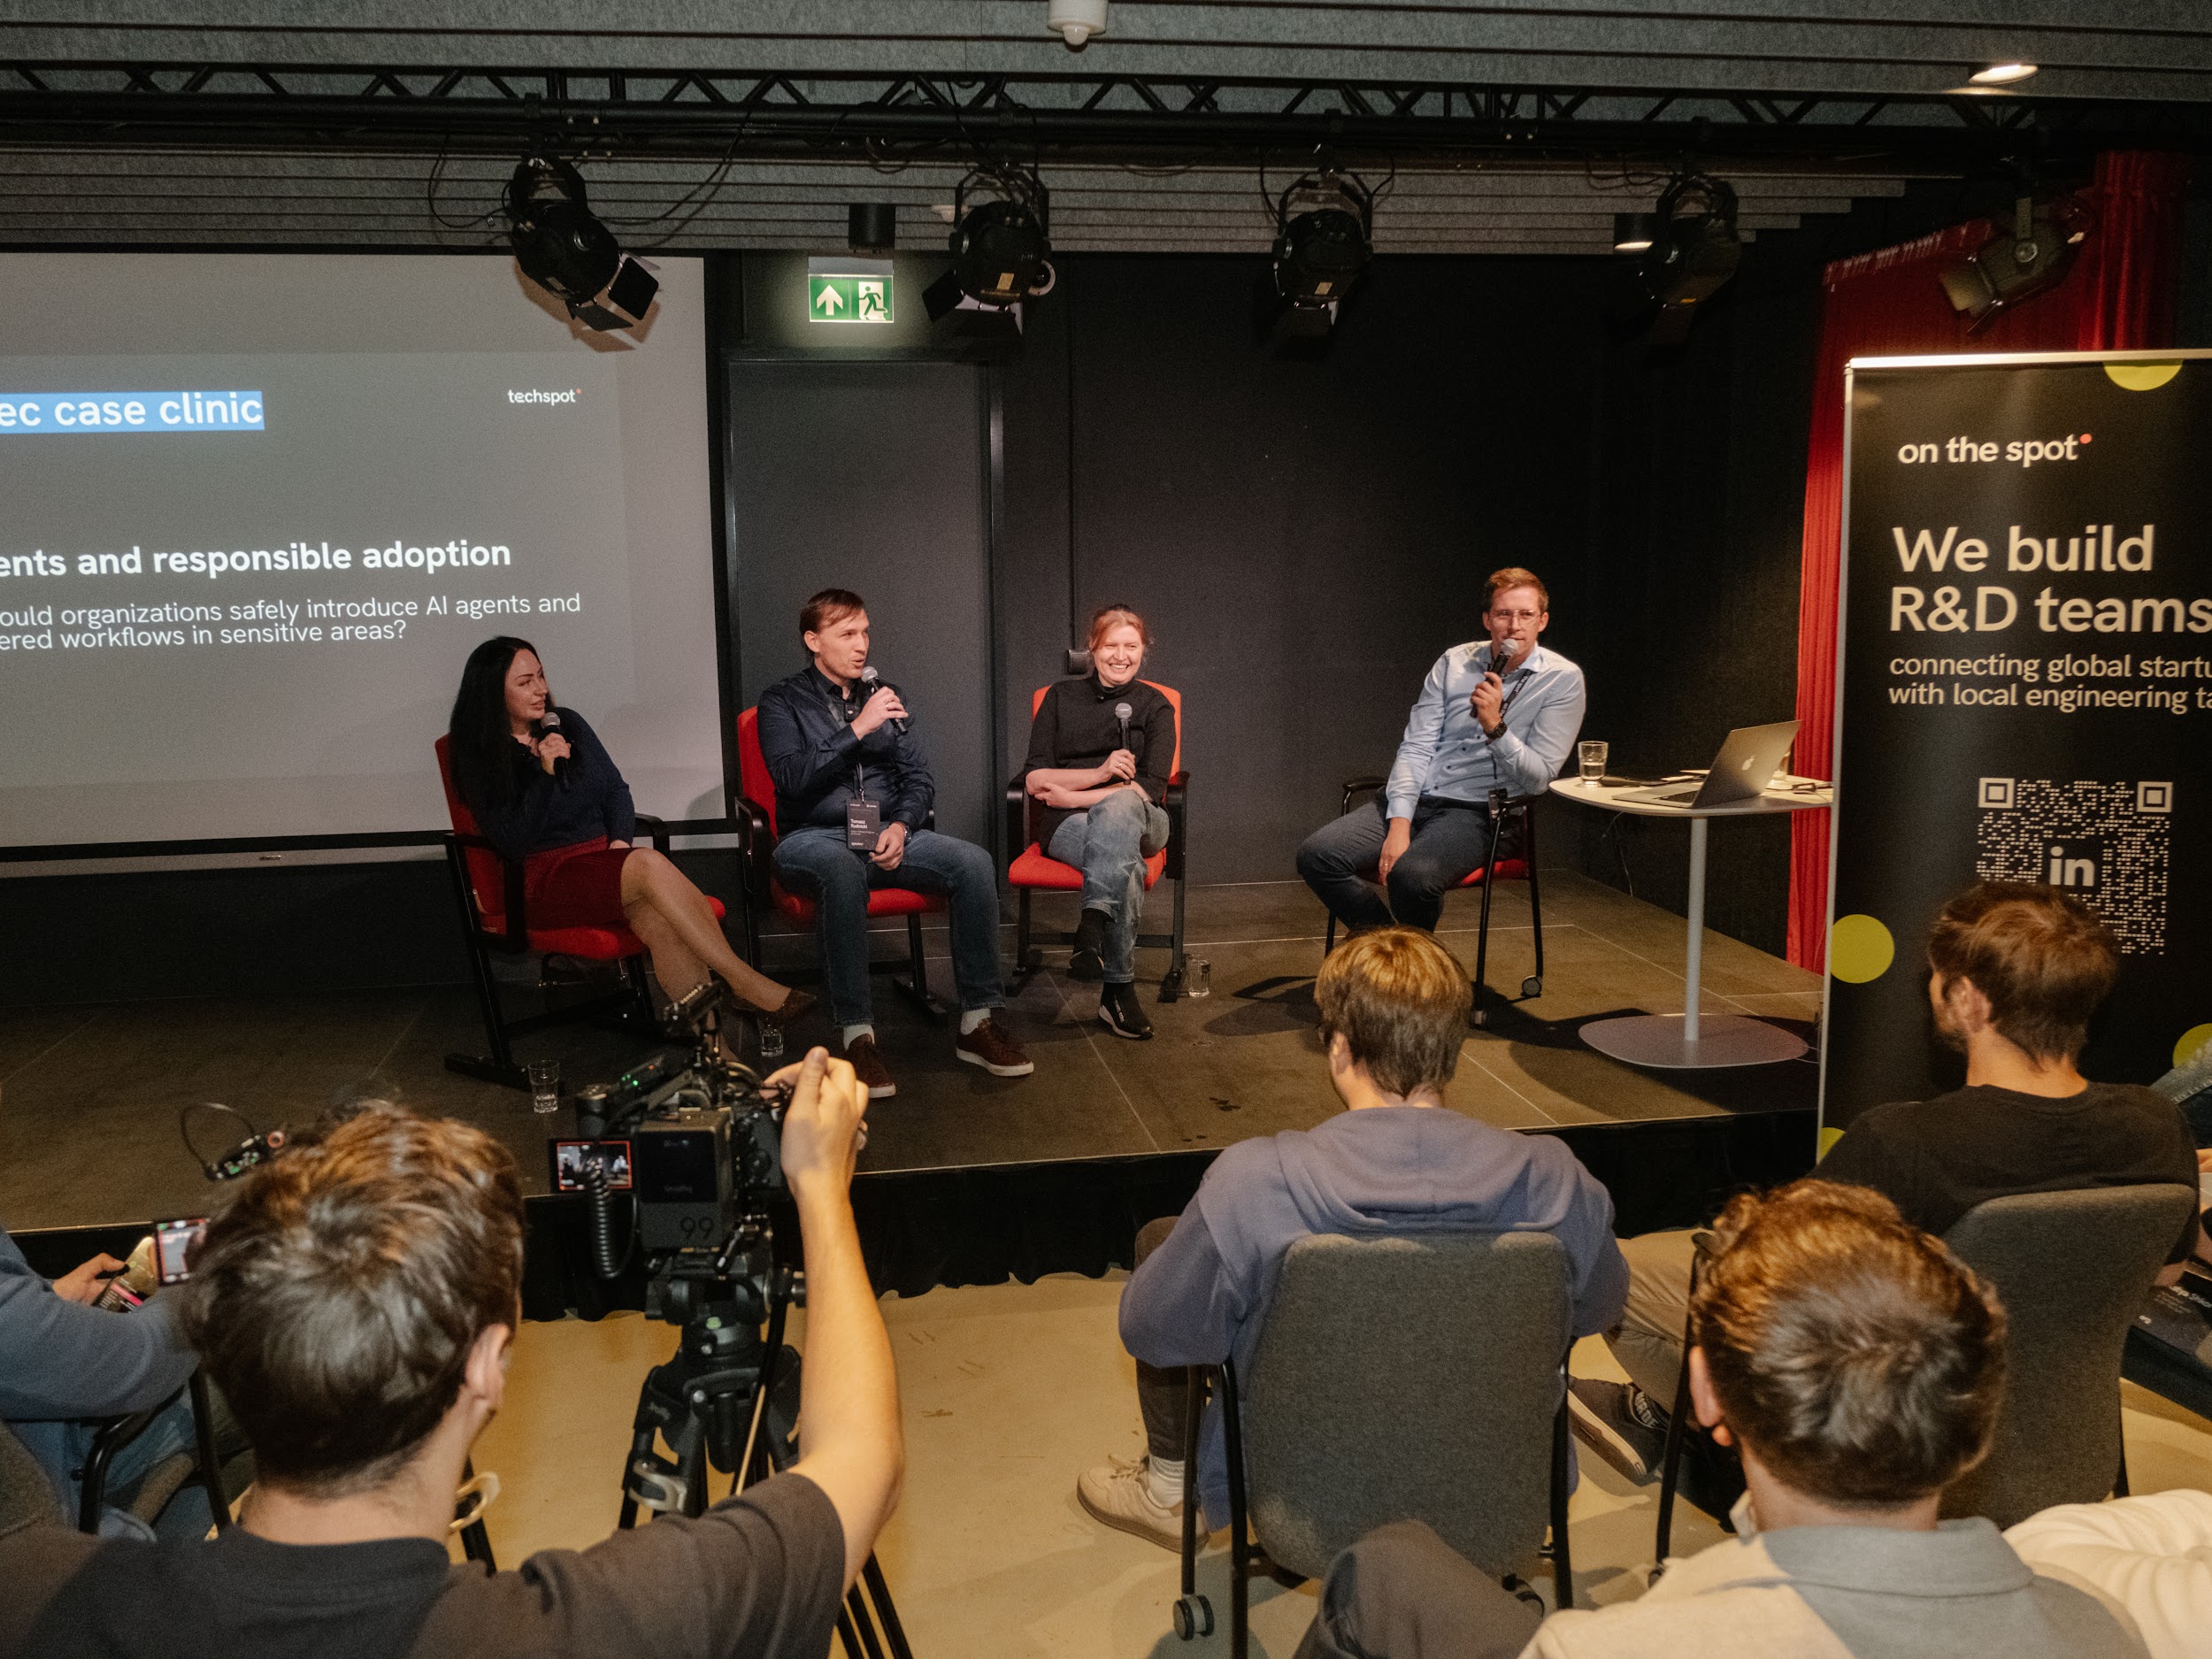
For a closer look at Cycode’s SAST, watch Tomasz Rudnicki’s TechSpot talk. Tomasz walks through taint-flow analysis, explains why static scanning can never be perfect, and shows where AI can help, but not replace SAST.
[/callout]
[slider-blog 7-10 | TechSpot meetup in Warsaw: On The Spot x Cycode]
2. Third-party integrations
The platform also connects to the tools customers already use and aggregates findings from:
- source code repositories
- CI/CD pipelines
- cloud environments
- IaC configurations
- package registries
- AI coding tools
It brings all findings into one place and adds the context needed to understand what each issue is and where it originated.
How it all came together
Funny enough, our founders didn’t start with a grand plan to build an all-in-one platform. It grew layer by layer.
Dor Atias, our CPO and Co-Founder, says:
The first thing we wanted to do was protect source control. We identified gaps in SCM platforms like GitHub, GitLab, and Bitbucket that no other companies were solving.
Then we enhanced the product to protect against hard-coded secrets.
Then came CI/CD protection.
Eventually we coined the term 'software supply chain security.'
One step led to another, and somewhere along the way we ended up with what we are today.
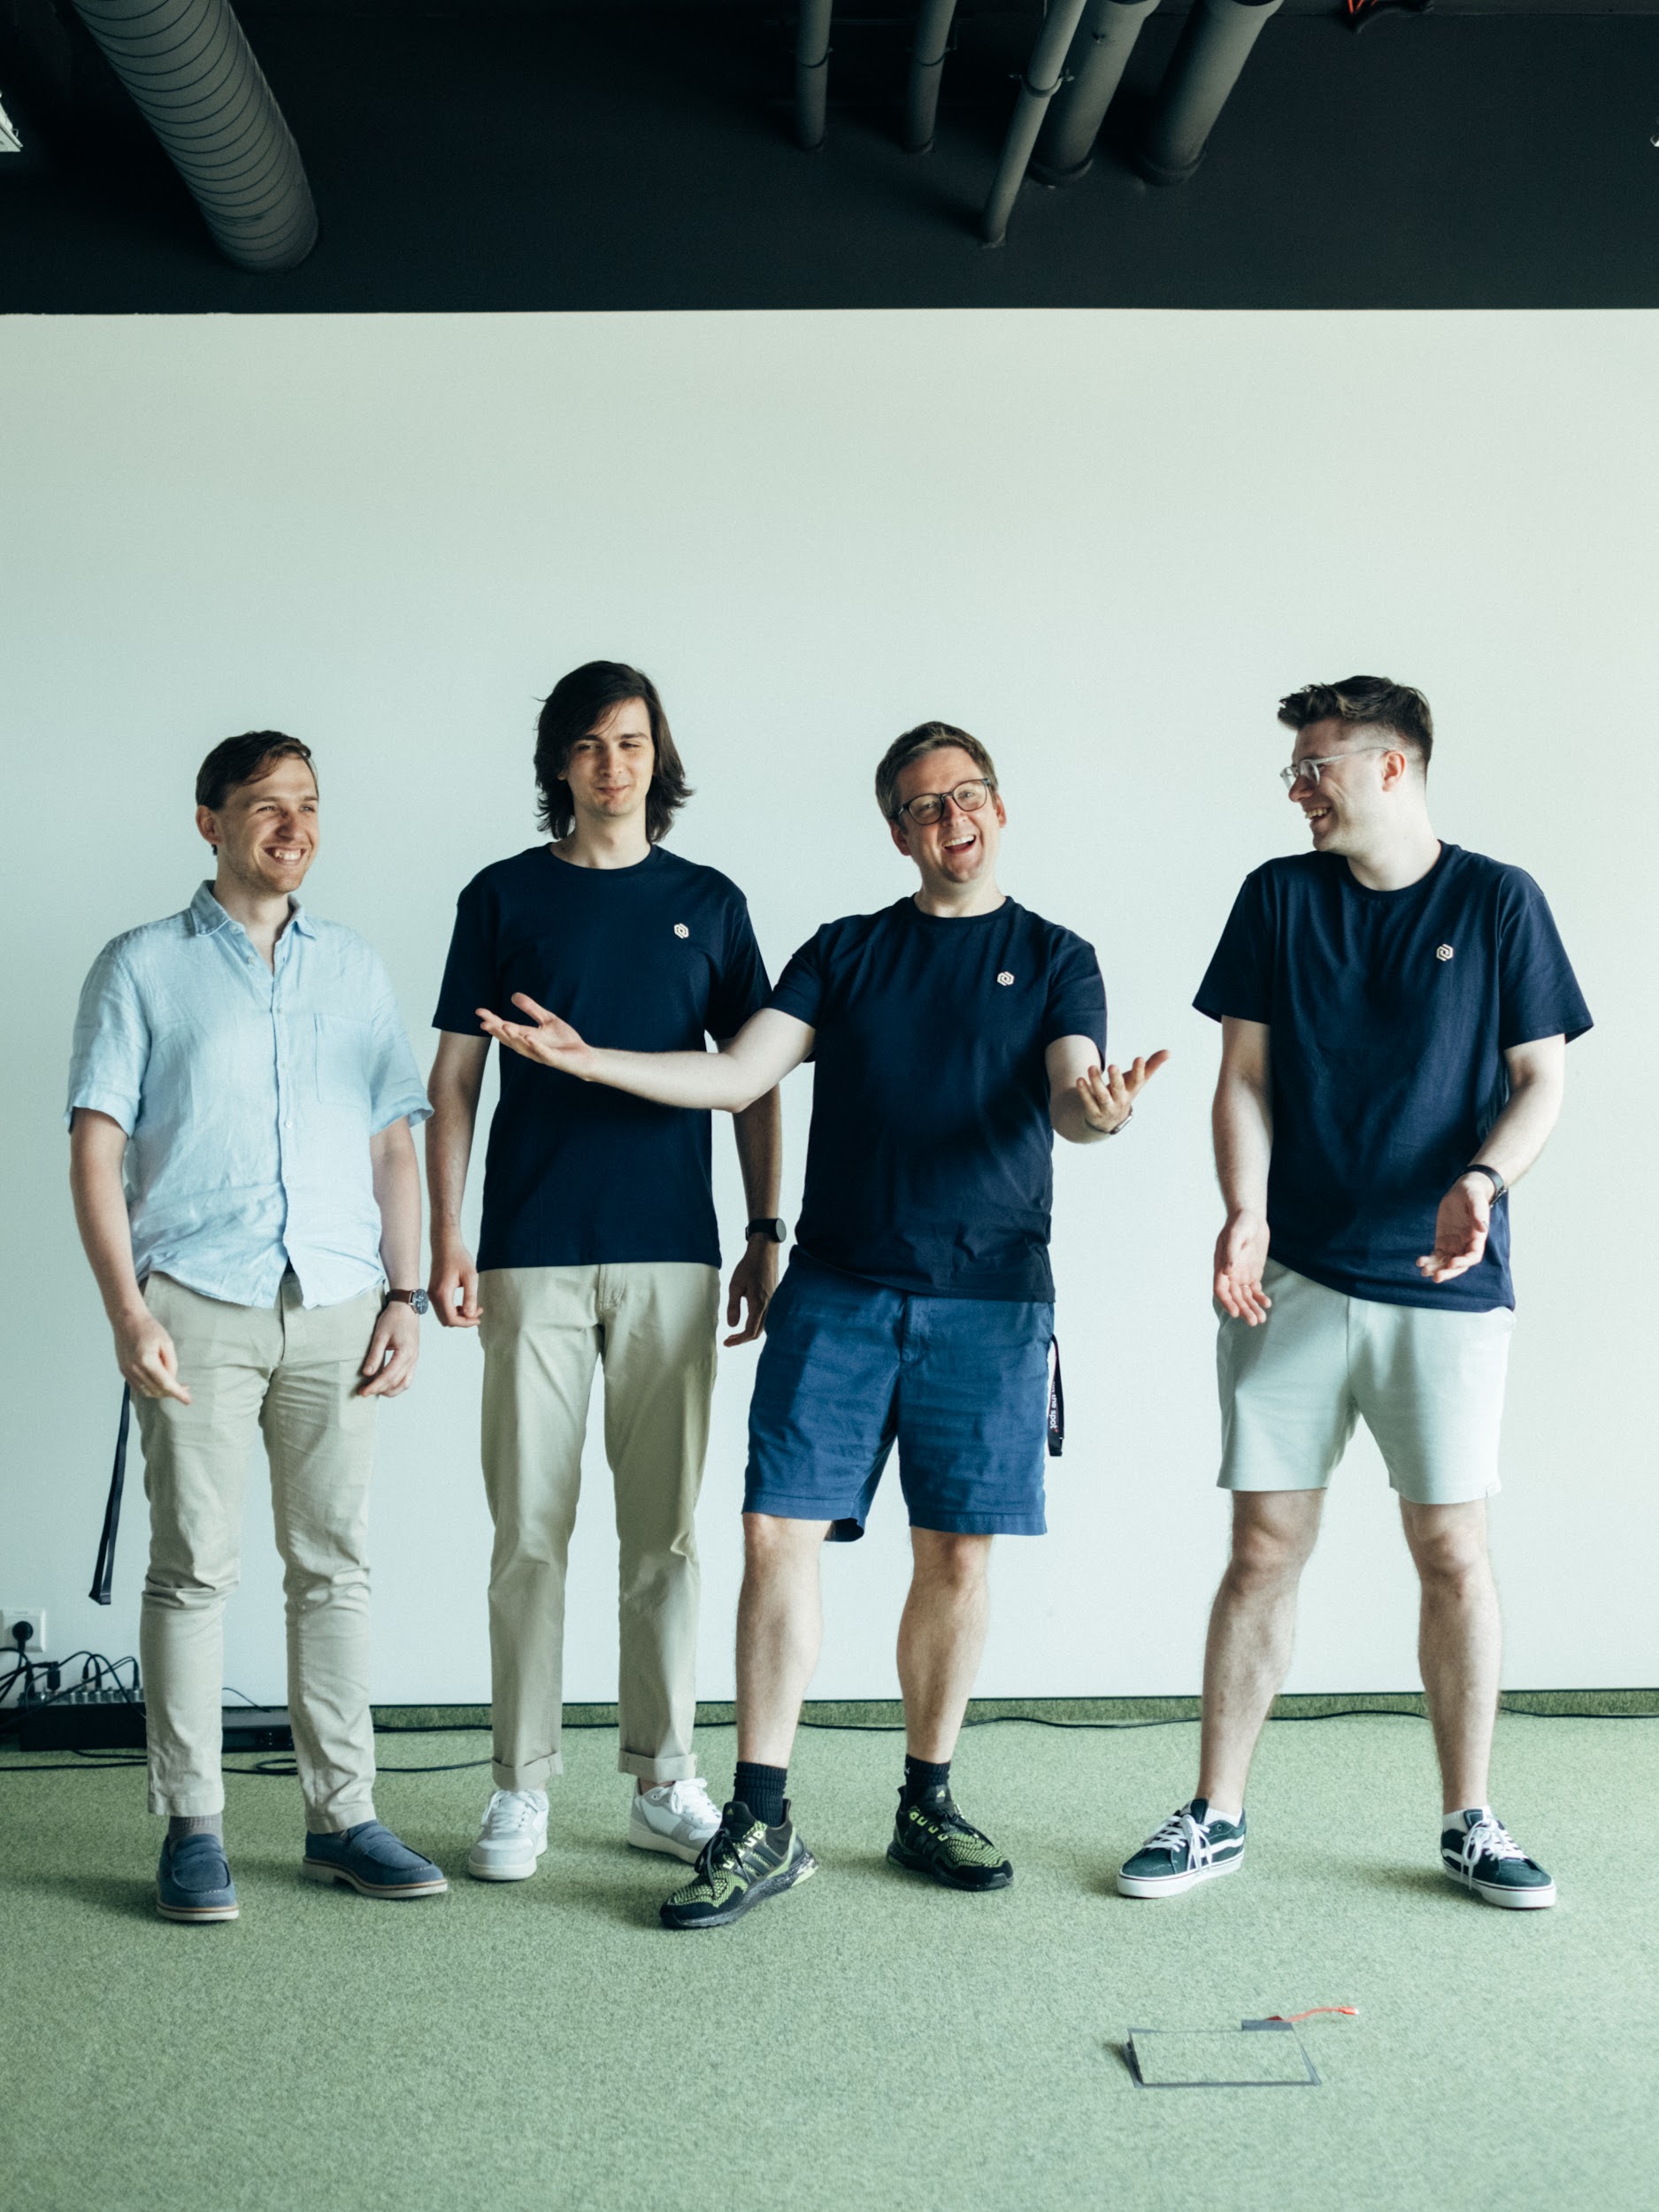
[slider-blog 11-12 | Cycode team and Dor Atias in Warsaw ]
As of September 2026, we call our product an Agentic Development Security Platform.
What will it turn into next? Nobody can say for sure. That's the reality of building security products in the middle of the AI shift.
The context layer: Context Intelligence Graph
To connect all signals across the development environment, Cycode uses its Context Intelligence Graph.
It helps with:
• Meaningful prioritization
Instead of treating every potential vulnerability equally, Cycode uses context to understand which issues can actually affect the application.
Developers can be sure that when an alert shows up, it’s worth their time.
• Practical remediation
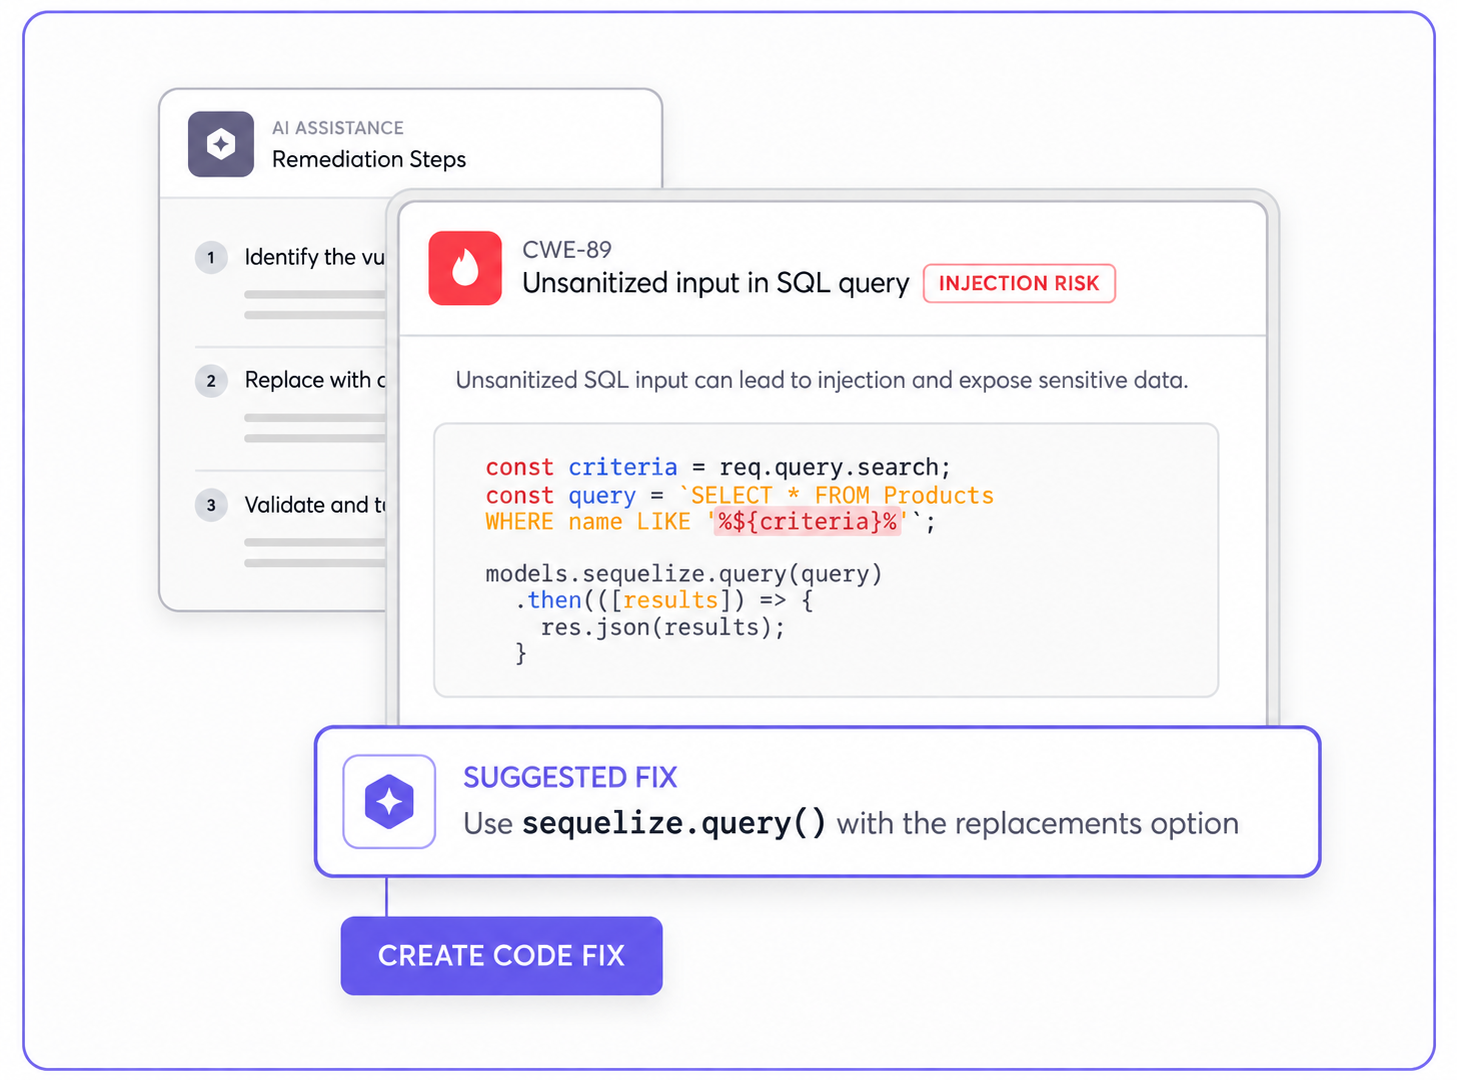
Being developers ourselves, we’re not exactly fond of the approach like “you have a vulnerability, fix it”. In the case with Cycode, fixing the issue only requires clicking one button.
Cycode Maestro, our orchestration engine, coordinates AI agents to analyze findings, determine what needs to change, and generate PR-ready fixes.
The platform integrates with development workflows. Security guidance shows up in your IDE, PR reviews come with automated checks, and CI/CD pipelines run scans without slowing anything down.
Open-source ecosystem & free tools to try
To get a feel for how we think and build things, you can check out the open-source tools we maintain as part of the CyGives initiative. They’re also great if you want to secure your own project — for free:
• Bearer CLI
A production-grade code scanner supporting multiple languages that helps catch vulnerabilities early. Works as a CLI tool you can run locally or integrate into your CI/CD pipelines.
• Raven
A Neo4j-powered analyzer for auditing package dependencies and GitHub Actions workflows. Loved for deep dives into supply chain security.
• Cimon
An eBPF-powered, real-time monitor for GitHub Actions. No setup needed, just add it to your workflow and it starts catching supply chain attacks immediately.
All these tools can be found at cycode.com/cygives/.
How we build Cycode in Warsaw
Our Polish team is grown and built by On The Spot, a company that helps startups establish and grow offshore R&D teams.
At the moment, we have 20+ people in Warsaw working on Cycode across 8 distributed product teams. "Distributed" here means our engineers in Poland work closely with teammates across Israel and the UK.
[slider-blog 1-6 | Cycode team in Warsaw]
Each team owns a product area end to end — from integrations and the Bearer code-analysis engine to scanning capabilities and more — and can shape both what gets built and how.
An example of that is how we implemented the dark mode:
The platform UI didn’t have dark mode initially, but one of the guys kept talking about it. So our team hacked up an inverted version behind a feature flag just in 15 minutes.
When the Israeli management saw it, they loved the idea, refined it, and added dark mode in the next release.
Feel our mood
Even though Cycode is now a Leader in the 2026 Gartner® Magic Quadrant™ for Software Supply Chain Security, we’re still very much in startup mode.
We don’t know what we’ll be doing in the next quarter, let alone one, two years from now. It’s not because we are wondering what to do, it’s because we have tons of things to do… It’s a competitive industry, so we need to deliver a lot of features and do it quickly.
– Dor Atias
The decision-making process is transparent and quick. If the pre-sales team lands a customer who needs a new feature, it will be live within a week or even a few days.
We look for people who are comfortable with ambiguity, take initiative, and move fast.
I always tell candidates: think of yourself like a stock. From the moment you join until the moment you leave (if you ever do), your value will have increased significantly. I see it all the time — people come in already experienced but after a few years they are much more professional, not afraid of challenges, and really know how to get the job done.
– Dor Atias
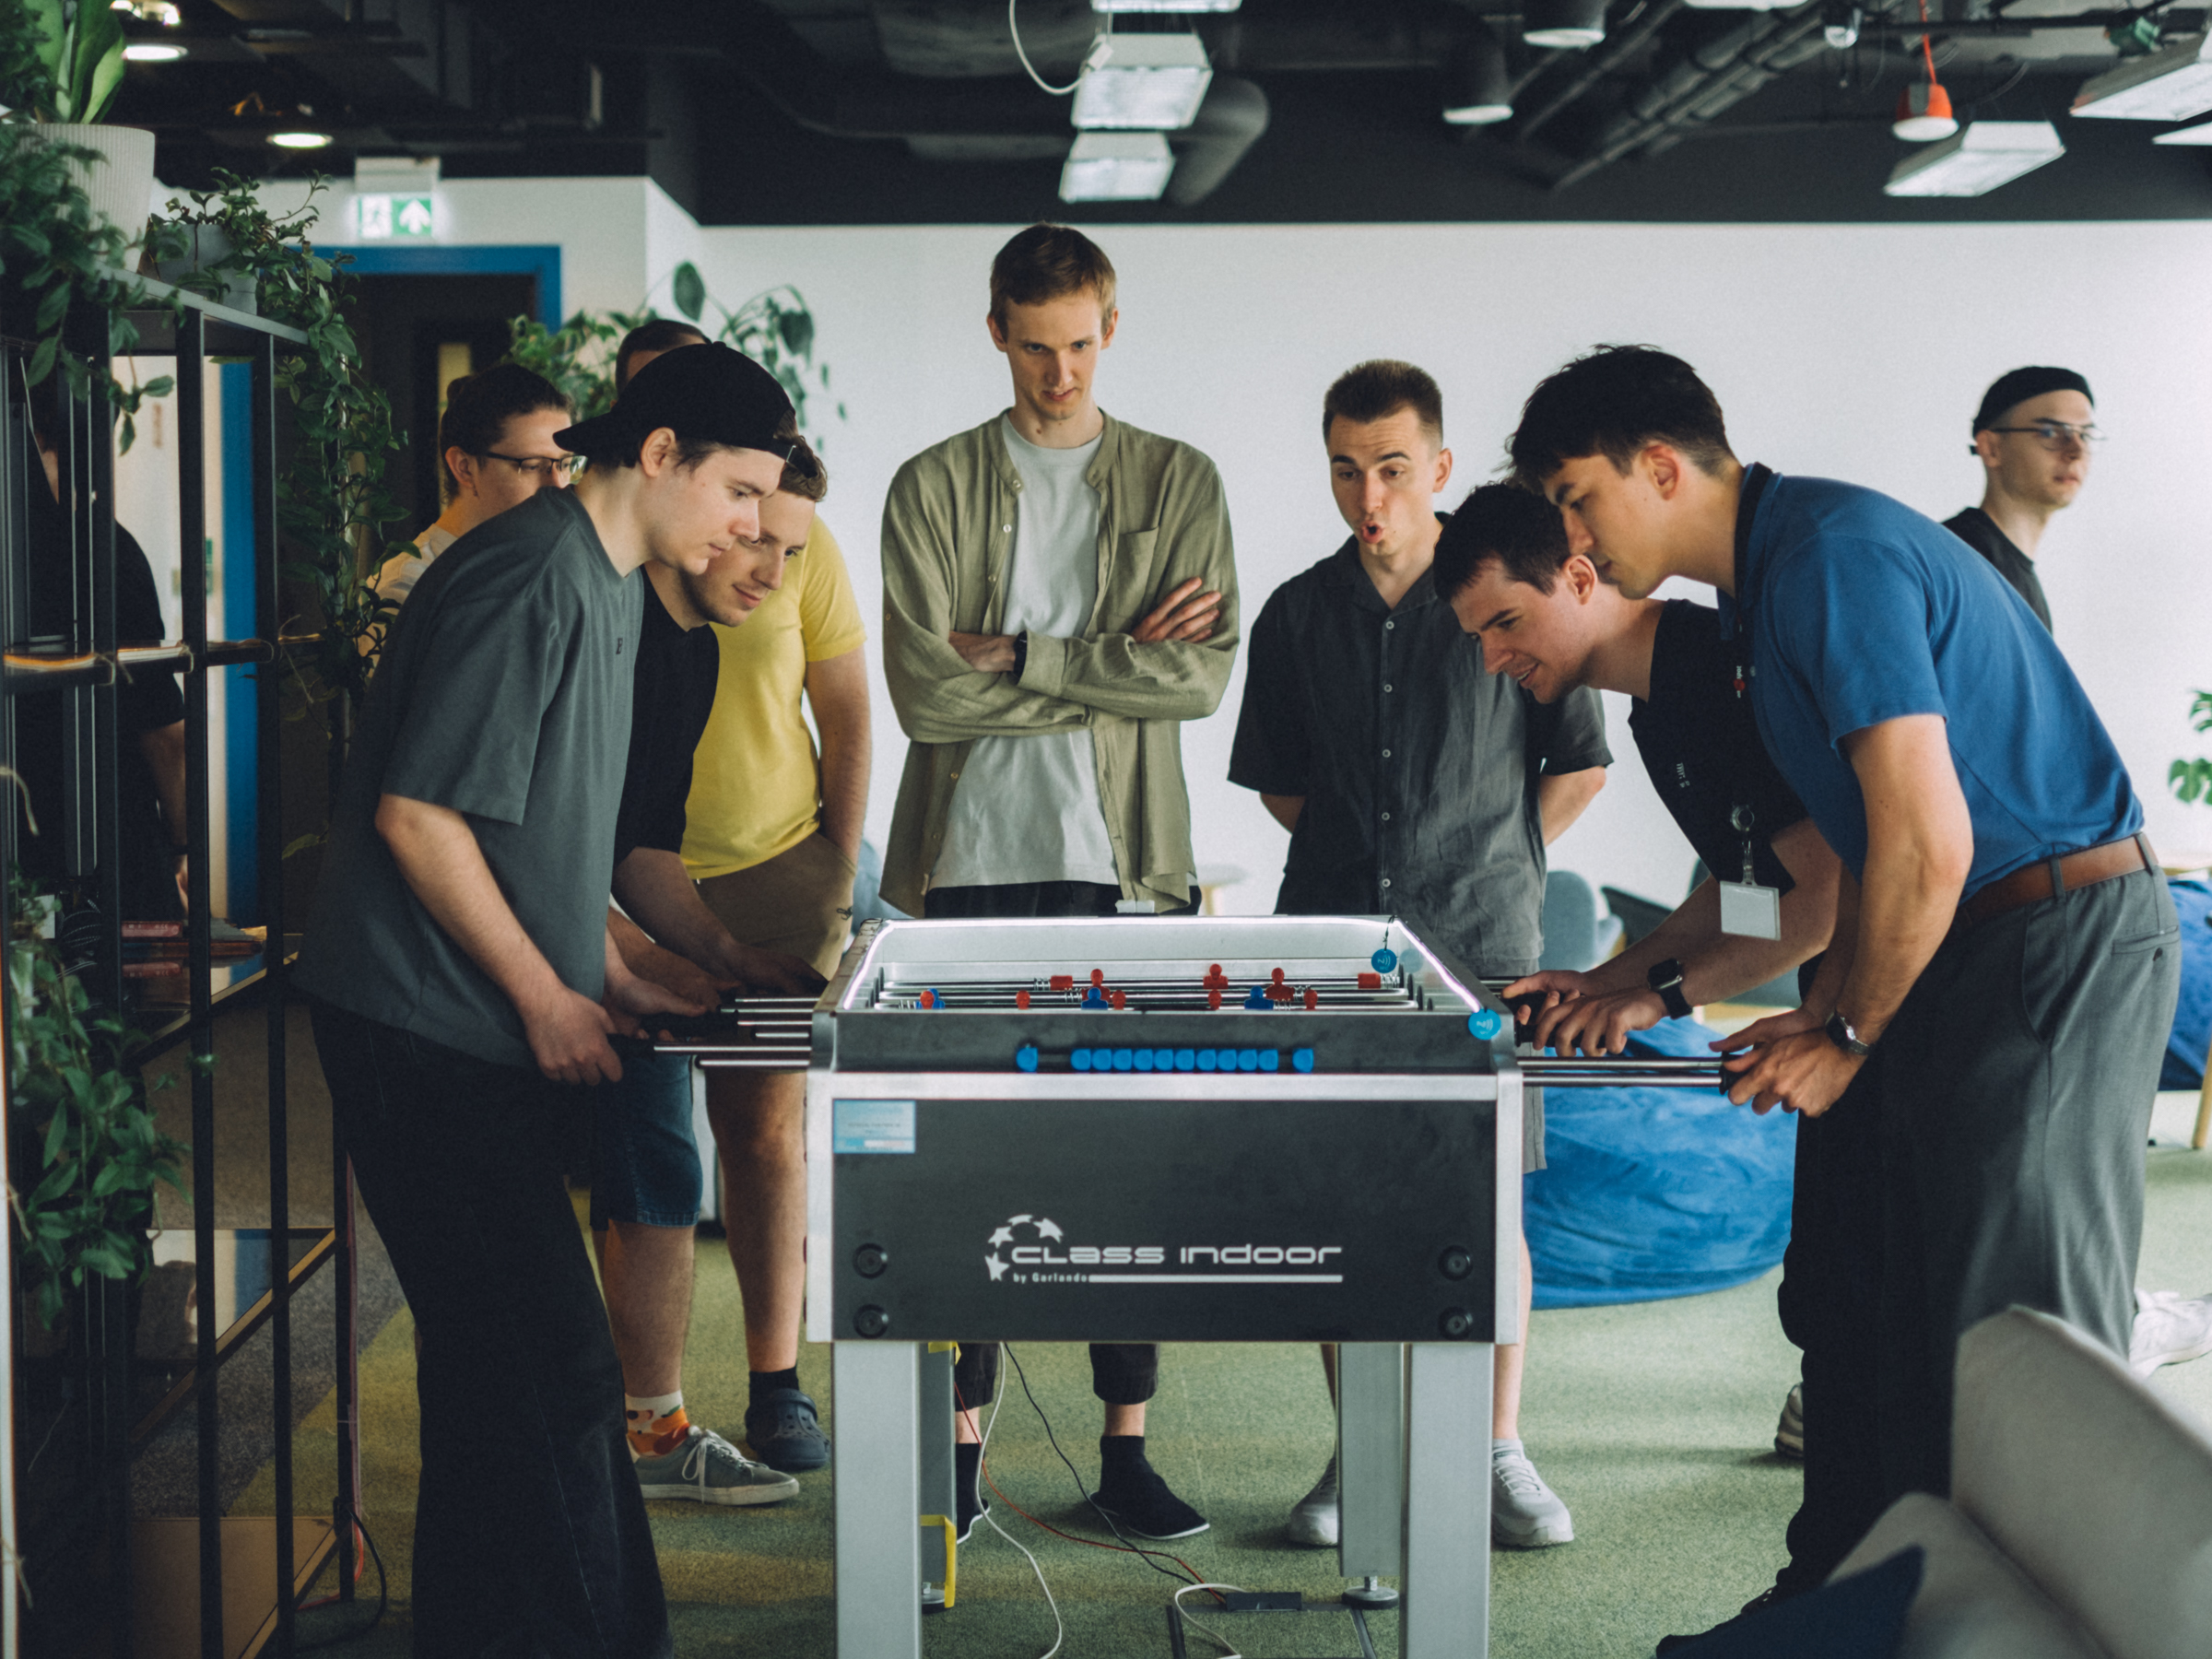
In October 2023, we moved from fully remote to hybrid work format. That works for us well: we know each other face to face, there are no barriers asking questions or discussing things, even if you’re speaking with someone on another domain team.
Small talk happens naturally, and relationships develop beyond the work itself. You can have a holy war over code quality and code style in person — that's a team favorite. The atmosphere is very friendly and relaxed.
[slider-blog 13-16 | Cycode teambuilding in Warsaw]
Open positions
Right now, On The Spot is growing Cycode's R&D team in Warsaw.
See the open positions.
Also, check out the talk on modern SAST-scanners by Cycode’s Engineer, Tomasz Rudnicki.

Stay in tune
with On The Spot
You've successfully signed up for our newsletter. Keep an eye on your inbox.
Read more
Discover what else is happening at On The Spot

TechSpot
Tech events in Poland and online for everyone interested in software architecture and systems design. Like-minded people, top experts from leading companies, and a big engineering community.


137 Podcast
Conversations with top engineers, CTOs, and founders about day-to-day engineering and everything that excites us about tech.